Category
Cybersecurity
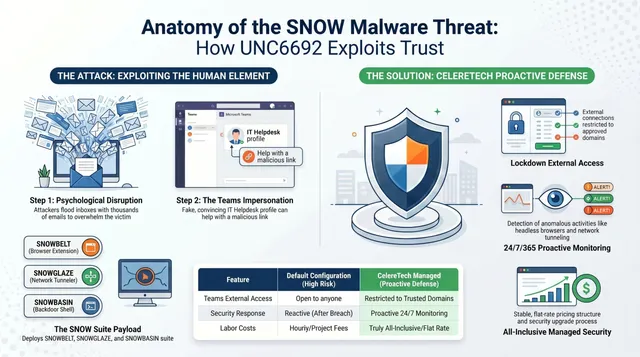
The SNOW Malware Suite: How UNC6692 Is Exploiting Microsoft Teams to Attack Businesses in 2026
The SNOWBELT, SNOWGLAZE, and SNOWBASIN malware components used by threat group UNC6692 give attackers persistent network access through a trusted Microsoft Teams support scam, not a software exploit.
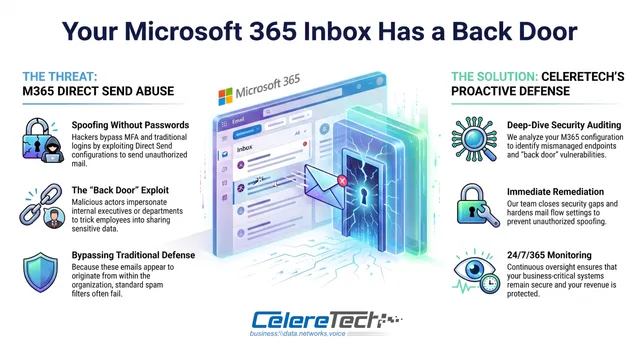
The Microsoft 365 Back Door Attackers Are Actively Exploiting — And How to Close It
Microsoft 365 Direct Send abuse lets attackers spoof internal-looking emails without compromising a single password, by exploiting a legitimate mail-relay feature most admins have never disabled.
Collaboration Tools: Easy for Teams, Easy Targets for Hackers
71% of remote workers have shared sensitive information through Teams, Slack, or similar apps — proper permissions, DLP policies, and training keep collaboration tools from becoming an attack vector.

Microsoft 365 Security Best Practices for SMBs: The Complete 2026 Guide
A comprehensive, step-by-step Microsoft 365 security guide for SMBs — identity, admin protection, email authentication, data loss prevention, device management, and backup, with the exact settings to configure.

Cybersecurity Services for Chicago Small Businesses: What to Look for and What It Costs
What cybersecurity services actually cost for a small business in Chicago, what should be included by default, and the red flags to watch for when evaluating a provider.

Zero Trust Security Explained: Why 'Never Trust, Always Verify' Is Winning
61% of global organizations have already adopted Zero Trust — a model that verifies every user and device continuously instead of trusting anyone already inside the network, unlike legacy VPNs.

Are You Making These 5 Common Ransomware Defense Mistakes?
43% of cyberattacks target small businesses, and only 14% feel prepared to defend themselves — most successful attacks trace back to preventable mistakes like untested backups and missing MFA.

MFA for Small Businesses: Why a Simple Password Isn't Enough Anymore
81% of data breaches involve compromised passwords — multi-factor authentication blocks most account takeovers even when a password is stolen, and rolls out with minimal user friction.

MDR Services: Why Managed Detection & Response Should Be Your Security Backbone
The average ransomware attack now costs $2.73 million, and attacks launch every 11 seconds — Managed Detection & Response pairs 24/7 monitoring with human analysts to catch what automated tools alone miss.

Your Expanding Attack Surface: What It Means and How to Defend It
Cloud attack surfaces have surged 600% in a single reporting period — Attack Surface Management continuously maps every exposed device, app, and cloud asset an attacker could target, not just the known ones.

XDR Explained: Next-Level Threat Defense for Modern SMBs
Cybercriminals launched 5.5 billion malware attacks in a single year — Extended Detection & Response (XDR) connects endpoint, email, and network defenses into one system so threats can't slip through the gaps.

What Is EDR? How Endpoint Detection & Response Shields Your Business
Cybercriminals spend an average of 287 days inside a network before being detected — Endpoint Detection & Response (EDR) monitors device behavior in real time to catch intrusions in hours, not months.

IoT: Keeping Your Connected World Safe
IoT connections are projected to reach 29 billion by 2027, and each connected device — cameras, thermostats, printers — is a potential entry point that needs its own network segmentation.

The Dark Web Can Be Tracked for Free With Google
Remote work has tripled since 2020, increasing the risk of company data leaking onto the dark web — Google offers a free monitoring tool that can catch exposed credentials early.

Unraveling Encryption: How It Works and Why It Matters
Encryption scrambles data using a mathematical key so only authorized parties can read it — the same core idea protects both stored passwords and data sent over a network.

Are Password Managers Really Safe?
65% of Americans don't trust password managers, yet security experts rely on them because an encrypted, audited manager is far safer than a reused or written-down password.